 GDPR / Data ProtectionHalloween offerBuy one licence, get the second free: £12.99 each · ends 31 OctAdd to basket
- 8lessons
- 1 hourto complete
- 1CPD hours
- October 2026last updated
When you need this course
- Your Data Security and Protection Toolkit is dueThe toolkit expects every member of staff to complete data security training each year. Every learner gets a dated certificate.
- There has been a data breach or a near missStaff learn to spot a breach, what to do straight away and who to tell.
- Staff use phones, apps or care softwareCovers devices, apps and paper records, plus fraud, scams and cyber security.
- Your annual refresher is dueAbout 1 hour online, with a certificate for each learner and a dashboard showing who has finished.
Try it: a real lesson and question from this course
Data protection law and principles
Personal data is any information that identifies a living person, directly or indirectly: a name, address, date of birth, room number, photograph, NHS number, or a description that makes it clear who someone is. Some personal data is special category data, which needs extra protection because misuse could cause serious harm. It includes information about a person's health, including their care, medicines and conditions, as well as racial or ethnic origin, religious beliefs, sexual orientation and genetic data. Almost everything you record in care is special category data.
The law is UK GDPR and the Data Protection Act 2018, as amended by the Data (Use and Access) Act 2025. The Information Commissioner's Office (ICO) regulates it. UK GDPR sets seven principles for handling personal data. It must be used lawfully, fairly and transparently. It must be collected for specified purposes and not used for something unrelated. It must be adequate, relevant and limited to what is needed. It must be accurate and kept up to date. It must be kept no longer than necessary. It must be kept secure. And the organisation must be able to show it complies, which is called accountability.
Your employer is the data controller and is responsible for how personal data is used. It must have a lawful basis for each use. In care, this is usually not consent: it is normally that the processing is needed to provide care, under a contract or a public task, with the specific condition in UK GDPR for health and social care. This means people cannot usually "opt out" of their care records, but they must be told how their information is used, in a privacy notice.
You have a personal responsibility too. Only access the information you need for your role, use it only for care, keep it secure, and follow your workplace's data protection policy. Looking up someone's records out of curiosity, even a colleague or neighbour, is a serious breach and can be a criminal offence. The ICO can fine organisations, and staff can face disciplinary action.
Which of these is personal data?
In the hub, a wrong answer sends the staff member a short follow-up lesson and a fresh question on the same point. They close the gap before they can finish the module, and every attempt is recorded for your CQC evidence.
Next: one of the course's interactive activities, exactly as your staff get it.
Try it yourself
CareStream InteractiveThe data protection principles
Match each UK GDPR principle to what it means in care.
Tap a term on the left, then its meaning on the right
Term
Meaning
This exercise is here to help you practise — it is not marked and does not affect your result.
That is how the training works. Give your whole team the full GDPR / Data Protection module.
What the course covers: 8 lessons
- Data protection law and principles
- Confidentiality and the Caldicott Principles
- People's rights over their information
- Sharing information safely
- Recording, storing and disposing of information
- Fraud, scams and cyber security
- Devices, apps and paper records
- Data breaches
Assessment and certificate
- 32 question assessment with a pass mark of 80%.
- A follow-up lesson on anything a learner gets wrong, so the gaps are closed, not just scored.
- A named, dated certificate the moment they pass, carrying the CPD Certified mark and CPD hours, ready to download as a PDF.
- Kept on their training record in your dashboard, ready for your CQC evidence.
Free GDPR / Data Protection resources
Official guidance from Skills for Care, free to download. Useful alongside the course.
- Skills for Care: statutory and mandatory training guideWhat Skills for Care expect every course on this subject to cover, and how often.
- NHS England: Data Security and Protection ToolkitWhere care providers complete their yearly toolkit, including staff training.
- ICO: guide to the data protection principlesThe Information Commissioner’s guide to the principles the course is built on.
Specialists in the technology behind it all
The same technology behind the world's best products powers CareStream, so your team's gdpr / data protection training stays accurate, always up to date with the latest guidance, and is delivered in over 60 languages.
Avg. Duration
About 1 hour
Certificate
For every staff member
Available Languages (60+)
CPD Certified Course
A clear, practical grounding in gdpr / data protection.
Eight short lessons, each with a care scenario, an interactive activity and a quick check with an explanation. You start with a five question knowledge check so your learning gain can be measured, and finish with a 32 question assessment with a pass mark of 80%. The Data Security and Protection Toolkit expects staff to complete data security training every year.
By the end, your staff will be able to:
- Explain the UK GDPR data protection principles and why health and care information is special category data
- Apply the Caldicott Principles and the duty of confidentiality when using and sharing information
- Describe people's rights over their information, including access requests and complaints, and how to respond
- Record, store, share and dispose of personal information securely, on paper and digitally
- Recognise cyber threats such as phishing and scams, and use devices, passwords and messaging safely
- Recognise a data breach, including data received in error, and report it immediately
A closer look at the gdpr / data protection module.
The module is built in short, practical sections. Each one teaches a part of the topic, then applies it to a real care scenario and checks understanding before moving on.
Data protection law and principles
Personal data is any information that identifies a living person, directly or indirectly: a name, address, date of birth, room number, photograph, NHS number, or a description that makes it clear who someone is. Some personal data is special category data, which needs extra protection because misuse could cause serious harm. It includes information about a person's health, including their care, medicines and conditions, as well as racial or ethnic origin, religious beliefs, sexual orientation and genetic data. Almost everything you record in care is special category data. The law is UK GDPR and the Data Protection Act 2018, as amended by the Data (Use and Access) Act 2025. The Information Commissioner's Office (ICO) regulates it. UK GDPR sets seven principles for handling personal data. It must be used lawfully, fairly and transparently. It must be collected for specified purposes and not used for something unrelated. It must be adequate, relevant and limited to what is needed. It must be accurate and kept up to date. It must be kept no longer than necessary. It must be kept secure. And the organisation must be able to show it complies, which is called accountability. Your employer is the data controller and is responsible for how personal data is used. It must have a lawful basis for each use. In care, this is usually not consent: it is normally that the processing is needed to provide care, under a contract or a public task, with the specific condition in UK GDPR for health and social care. This means people cannot usually "opt out" of their care records, but they must be told how their information is used, in a privacy notice. You have a personal responsibility too. Only access the information you need for your role, use it only for care, keep it secure, and follow your workplace's data protection policy. Looking up someone's records out of curiosity, even a colleague or neighbour, is a serious breach and can be a criminal offence. The ICO can fine organisations, and staff can face disciplinary action.
Confidentiality and the Caldicott Principles
Alongside data protection law, the common law duty of confidentiality means information given in confidence, such as details of a person's health and care, should not be shared without the person's consent unless there is a legal requirement or a clear justification, such as protecting someone from serious harm. The National Data Guardian's eight Caldicott Principles guide how confidential information is used in health and social care. First, justify the purpose for using confidential information. Second, use it only when it is necessary. Third, use the minimum necessary. Fourth, access should be on a strict need to know basis. Fifth, everyone with access must understand their responsibilities. Sixth, comply with the law. Seventh, the duty to share information for individual care is as important as the duty to protect confidentiality. Eighth, inform people about how their confidential information is used. The seventh principle matters in care. Failing to share information can harm people, for example if a hospital is not told about a person's allergies, or a district nurse is not told about a pressure sore. Sharing relevant information with other professionals involved in someone's care, for their care, is normally expected and lawful. If you are unsure whether to share, ask your manager or data protection lead, but do not let uncertainty put someone at risk. Safeguarding is a clear example. If you believe a person is at risk of abuse or neglect, you must share the information needed to protect them through your safeguarding procedure, even without consent. Data protection law does not stop this. Confidentiality also applies to conversations. Do not discuss people you support in public places, on social media, or with your own friends and family, even without using names, because details can still identify them.
People's rights over their information
People have rights over their personal information under UK GDPR. They have the right to be informed about how it is used, usually through a privacy notice. They have the right of access, to see and get a copy of their information, called a subject access request. They have the right to have inaccurate information corrected, and in some circumstances the rights to have information erased, to restrict or object to how it is used, and to move it to another organisation. A subject access request can be made verbally or in writing, to anyone in the organisation, and does not have to use particular words. If someone asks you for a copy of their records, or says "I want to see what you have written about me", pass it to your manager or data protection lead straight away, recording the date. The organisation normally has one month to respond, which can be extended in some cases. Since the Data (Use and Access) Act 2025, the clock can be paused while the organisation asks for information it genuinely needs, such as proof of identity, and it only has to make reasonable and proportionate searches. Other people may ask for someone's information: relatives, friends or other organisations. Relatives do not automatically have a right to see a person's records. They may have legal authority, such as a registered lasting power of attorney that covers the decision, or the person may consent to sharing. If not, refer the request to your manager. Records of people who have died are not covered by UK GDPR, but are still confidential, and access is handled under other law, such as the Access to Health Records Act 1990 for the personal representative. Refer these requests to your manager too. People also have the right to complain. Since the 2025 changes, organisations must make it easy to complain about how personal information has been used, acknowledge complaints within 30 days, and respond without undue delay. People can also complain to the ICO.
Sharing information safely
Before you share personal information, ask yourself: is there a good reason, does this person need to know for the person's care or safety, and am I sharing only what they need? Then share it securely. On the phone, check who you are speaking to before discussing anyone. Callers claiming to be relatives, professionals or the police may not be who they say. Take their details and call them back through a verified number, or check with the person or their care plan who information can be shared with. Many services use a password or agreed contact list. By email, only use approved, secure email accounts, never personal ones. Check the recipient address carefully before sending, especially with autofill, which is one of the most common causes of breaches. Use secure email or encryption for personal information, as your workplace directs, and put only the minimum needed in the subject line. Messaging apps and social media need particular care. Only use apps your employer has approved for sharing care information. Never post anything about the people you support, their photographs or details of your work on personal social media, even in closed groups. Photographs of people you support may only be taken on approved devices, for an agreed purpose, with consent or a lawful reason. Conversations can be overheard. Do handovers in private spaces, keep your voice down, and avoid discussing people in corridors, lifts, shops or on public transport. In people's own homes, be careful what you say in front of visitors, and never leave notes where others can read them. When sharing with other organisations, such as a hospital, GP or local authority, follow your workplace's procedures, use secure methods, and record what was shared, with whom, when and why.
Recording, storing and disposing of information
Care records are vital for safe care and are a legal record of what happened. Write records accurately, clearly and promptly, ideally at the time or as soon as possible afterwards. Record facts, what you saw, heard and did, and the person's own words where relevant, not opinions or judgements. Use respectful language, because people have the right to read what is written about them. If you make an error, correct it as your system allows, without deleting or obscuring the original. Store information securely. Digital care records should only be accessed on approved devices, with your own login. Lock your screen whenever you step away and log out at the end of your shift. Paper records, such as medicine charts, handover sheets and care plans, should be kept in a locked cabinet or office when not in use, and never left on corridors, in lounges, in cars, or in people's homes where they are not meant to be kept. Keep information only as long as it is needed. Your organisation has a retention schedule, guided by the national records management code of practice for health and social care, setting how long each type of record is kept. Do not create extra copies, such as personal notebooks or photos of handover sheets on your phone. Dispose of information securely. Paper containing personal information goes in the confidential waste bin or shredder, never the ordinary bin or recycling. This includes handover notes, drafts, labels from medicine bottles and old lists. Devices and storage are disposed of by your IT provider so data cannot be recovered. Clear desk and clear screen habits help: at the end of each task, put papers away, close records and lock the screen.
Fraud, scams and cyber security
Care organisations hold valuable information and are targeted by criminals. Most cyber attacks start with people, not technology, so your actions are the most important defence. Phishing is when criminals send emails, texts or messages pretending to be someone trusted, such as your manager, a supplier, a bank, the NHS or IT support, to trick you into clicking a link, opening an attachment, entering your password or sending money or information. Warning signs include urgency or pressure ("act now or your account will close"), requests for passwords or payment, unexpected attachments, slightly wrong email addresses or links, poor spelling, and offers that seem too good to be true. Phone calls, called vishing, use the same tricks. Stop, check and report. Do not click links or open attachments you are not expecting. Check with the sender using contact details you already have, not those in the message. Report suspicious messages to your manager or IT support, following your workplace's procedure. If you have already clicked or entered details, report it immediately; speed limits the damage, and you will not be blamed for reporting honestly. Passwords protect everything. Use a strong password for each system, such as three random words, never reuse your work password elsewhere, and never share your login, even with a colleague or manager. Use multi factor authentication where it is available. Everything done under your login is recorded as you. Install updates when prompted, only use approved software and apps, and never plug unknown USB sticks into work devices. Ransomware, which locks systems and records until a payment is made, can stop you accessing care plans and medicine records, so good security protects the people you support as well as their information. People you support can also be targeted by scams by phone, post, email or doorstep. Be alert and report concerns through your safeguarding procedure.
Devices, apps and paper records
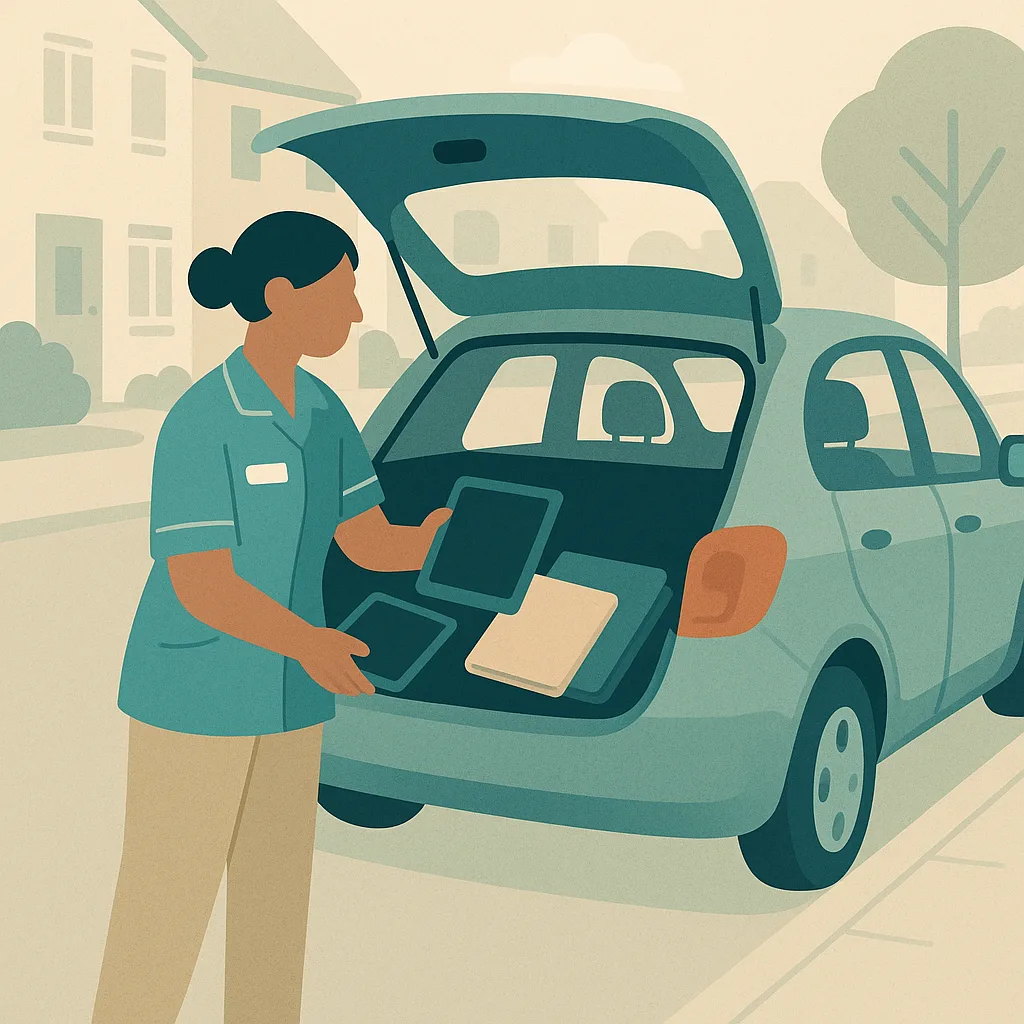
Work phones, tablets and laptops hold or give access to a great deal of personal information. Keep them with you or locked away, use a PIN or password lock, and never let anyone else, including family, use them. Do not store care information on personal devices unless your employer has approved it and it is secured. If a work device is lost or stolen, report it immediately so it can be locked or wiped remotely. Home care and community workers carry information between visits. Take only what you need, keep papers and devices out of sight and locked in the boot of your car rather than on the seat, never leave them in a car overnight, and do not leave notes about other people in someone's home. Take care when using devices in public places, where screens can be overlooked. Messaging apps are convenient but risky. Only use apps your employer has approved for care information, and follow its rules. Messages sent to the wrong group or person, screenshots, and messages left on personal phones after someone leaves the job are common causes of breaches. Personal WhatsApp or similar groups should never be used to share information about the people you support unless your employer has formally approved and secured it. Paper records are still widely used. Keep medicine charts, care plans and daily notes in their proper place, close files when you are not using them, and never take records home. Make sure fax machines, printers and photocopiers are not left with documents on them. Remember physical security too. Keep offices and cabinets locked, do not let unknown visitors into staff areas, and challenge politely anyone you do not recognise who is looking at records.
Data breaches
A personal data breach is a security incident that affects the confidentiality, integrity or availability of personal data. Confidentiality breaches are when information is seen by or sent to someone who should not have it, such as an email to the wrong person, a lost handover sheet or someone accessing records without a reason. Integrity breaches are when information is changed or recorded incorrectly without authority, so it can no longer be trusted, such as notes written in the wrong person's record. Availability breaches are when information is lost or cannot be accessed, such as records destroyed in error or a system locked by ransomware. Receiving data in error is also important. If you are sent information that is not meant for you, such as another care provider's records or an email about someone you do not support, do not read further, do not forward it, tell the sender and your manager, and delete it as advised. If you think a breach has happened, report it immediately to your manager or data protection lead, however small it seems and even if it was your mistake. Do not try to cover it up or investigate it yourself. If you can safely contain it, do so, for example by asking the recipient of a misdirected email to delete it, retrieving lost papers or reporting a lost device so it can be wiped. Your organisation will assess the breach. If it is likely to result in a risk to people's rights and freedoms, it must be reported to the ICO within 72 hours of the organisation becoming aware of it; care providers using the Data Security and Protection Toolkit usually report through its incident reporting tool. If the risk to the people affected is high, they must be told without undue delay. Every breach is recorded, and the organisation learns from it to stop it happening again. Reporting quickly and honestly protects the people you support and is always the right thing to do.
The things your team must remember.
- Health and care information is special category data and needs extra protection
- Share on a need to know basis, but remember the duty to share can be as important as the duty to protect
- People have the right to see their information; pass access requests to your data protection lead straight away
- Lock screens, use strong passwords and never share logins
- Stop and check before clicking links or opening attachments; scams are often urgent and convincing
- Lock away paper records and use confidential waste; never leave records where others can see them
- Report a suspected breach immediately: your organisation may have to tell the ICO within 72 hours
Not a slideshow once a year. Training that sticks.
CareStream delivers gdpr / data protection training in the hub your team already uses, grounded in best practice and your own policies, so it fits your care setting and not a generic template.
Short teaching sections and a real care scenario, then an assessment that checks understanding.
Staff complete it in over 60 languages, while your records stay in English.
A wrong answer triggers a short follow-up lesson and a fresh question, so the gap is closed.
Automatic reminders at 90, 30 and 7 days, with a live compliance dashboard.
From your dashboard to your team, in the CareStream hub.
Training is delivered in the hub each staff member logs into. You allocate the modules, they complete them in their own language, and you get the completion records and certificates for your CQC evidence, with any gaps closed by automatic follow up training.
Assign GDPR / Data Protection to each staff member in seconds. No course builder and no setup for each person.
Staff work through the module on any device, in over 60 languages, teaching then checking understanding. A wrong answer sends a short follow up lesson.
See live completion status and a certificate for every person, ready as evidence for CQC.
Any step, in their language, in one tap.
Care teams are diverse and training should not leave anyone behind. On any lesson or question, a staff member taps the language button and the whole step flips into the language they think in. They understand it properly, and your records stay in English.
- One tap flips any lesson or question into their language, instantly.
- Over 60 languages, with no setup and no separate versions to manage.
- Completions and certificates stay in English for your CQC evidence.
Try the language buttons in the preview above.
Built for real learning, not box ticking
Every CareStream course goes further than a lesson and a quiz. These features come as standard on every course, giving your staff a richer way to learn and giving you the evidence to prove it.
Every course is built on recognised UK guidance and cites its sources, from NICE and Skills for Care to the NHS and the legislation itself.
A plain English glossary of the technical terms in each course. A simple way to support every learner, including staff with English as a second language.
A quick knowledge check before the lesson is compared with the final assessment, so every certificate comes with evidence of how much the course actually taught.
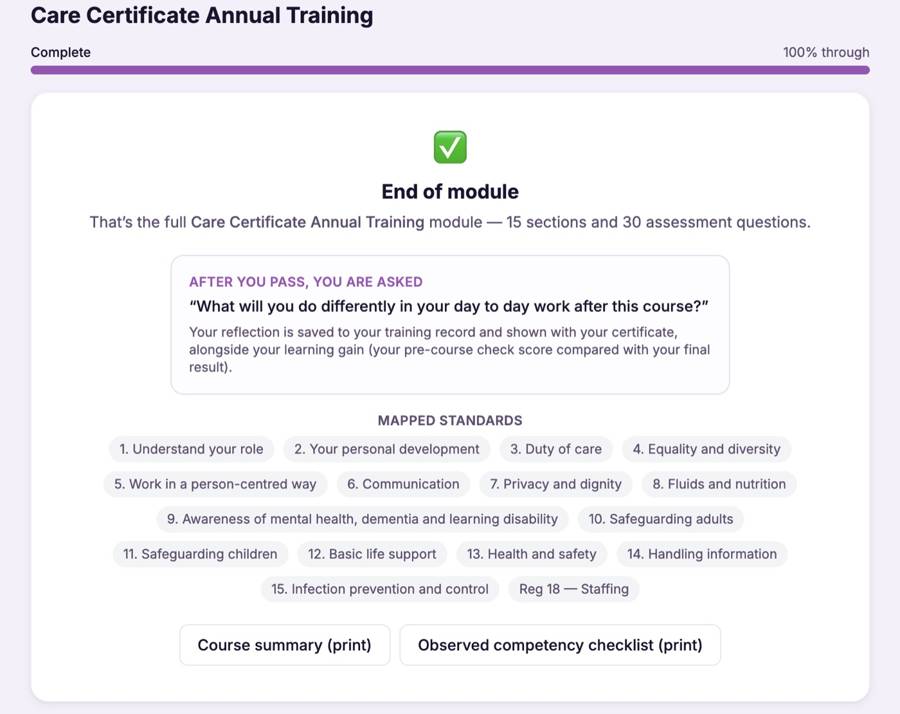
After passing, staff record what they will do differently in their day to day work. Their reflection is saved to their training record and shown with their certificate.
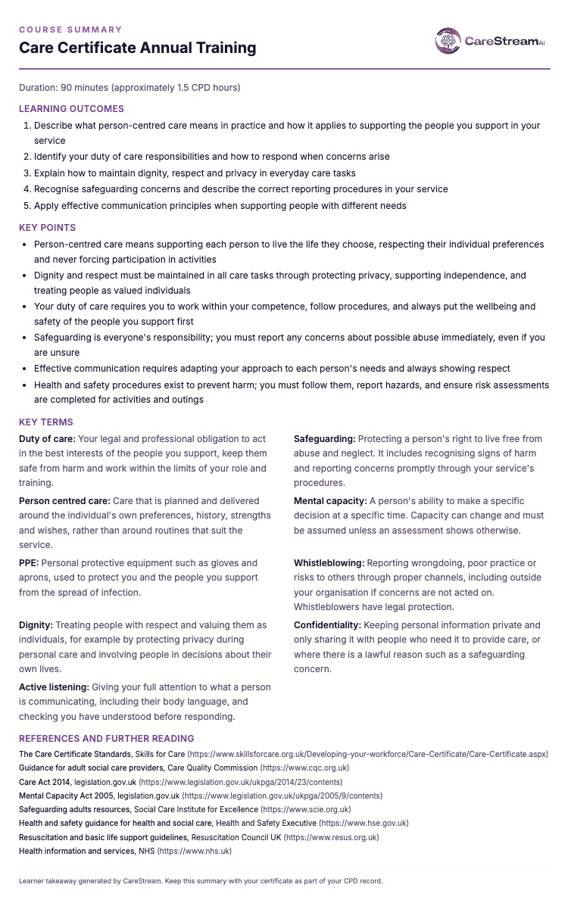
A printable one page takeaway of the outcomes, key points and key terms. Perfect for staff files, supervision conversations and the staff room wall.
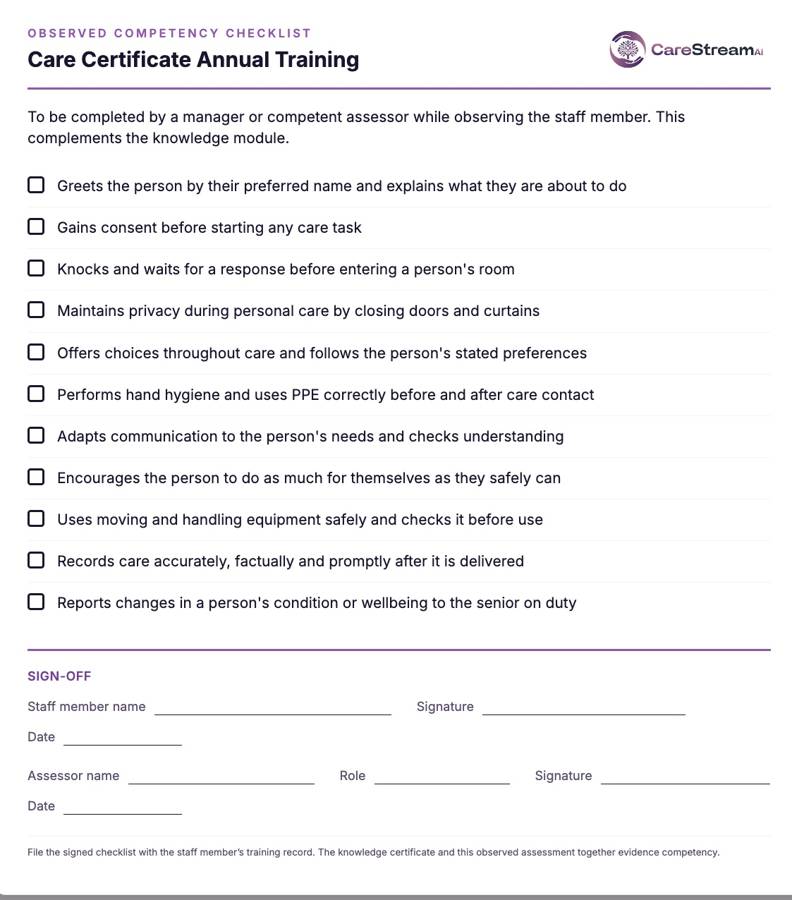
A printable checklist for managers to confirm skills in practice, with a sign off section. It completes the picture beyond the knowledge assessment.
Wrong answers become lessons, not failures
Most e learning marks an answer wrong and moves on. CareStream does not. Every wrong answer triggers an automatic follow up loop that teaches the point again and rechecks it, so no knowledge gap is left behind.
A wrong answer immediately opens a short lesson explaining the point, so the gap is closed there and then.
A fresh question on the same point checks the lesson has landed. The loop repeats until it has.
Staff move on to the next module and their certificate once they genuinely know the answer, not just after one lucky guess.
Why choose CareStream?
Training built for the care sector, delivered the way busy teams actually learn.
- 90+ care-specific training courses
- Bitesize, engaging lessons your staff actually finish
- Mapped to the Care Certificate & CQC standards
- Available in 60+ languages
- Instant certificate on completion
- Flexible learning, anytime, on any device
- Content kept up to date with UK care regulations
- Time to complete: 1 hour
Frequently asked questions.
Is GDPR / Data Protection training mandatory in care settings?
How often should staff complete GDPR / Data Protection training?
Can CareStream deliver GDPR / Data Protection training in other languages?
Does the training include an assessment?
More CPD Certified training your team may need
Every course below is certified by The CPD Certification Service, delivered in the hub, in any language. Add any of these to your basket.
 One-off Certificate
Care Certificate
Annual refresher training across all 16 standards of the Care Certificate (March 2025). You will revisit every standard, from understanding your role and duty of care through person-centred working, communication, safeguarding, basic life support, health and safety, handling information and infection prevention and control, including the new standard on awareness of learning disability and autism. Each standard has a short lesson, a workplace scenario and a knowledge check, followed by a final assessment. Your knowledge certificate is issued once you pass the assessment and your manager has verified your observed competency assessment.
Bulk discounts from 10+ licences
 Annual Certificate
COSHH (Control of Substances Hazardous to Health)
Annual COSHH training for care, domestic, laundry, kitchen and maintenance staff in any adult social care setting. Built on the Control of Substances Hazardous to Health Regulations 2002 and Health and Safety Executive guidance, it covers what counts as a hazardous substance, how harm happens, hazard pictograms and safety data sheets, COSHH assessments and controls, safe use and storage, gloves and skin care, body fluids and medicines, and dealing with spills and exposure. Eight lessons with scenarios and activities, then a final assessment.
Bulk discounts from 10+ licences
 Annual Certificate
End of Life / Palliative Care
End of life and palliative care for care workers in care homes, nursing homes, home care and supported living, mapped to Tier 2 of the End of Life Care Core Skills Education and Training Framework and NICE guidance. It covers person centred end of life care, communication, advance care planning and the law, recognising the last days of life, symptoms and comfort, emotional, spiritual and cultural needs, supporting families and bereavement, and care after death and your own wellbeing. Eight lessons with scenarios and activities, then a final assessment.
Bulk discounts from 10+ licences
 Annual Certificate
Food Hygiene
Annual food hygiene refresher for care workers who prepare, handle or serve food, or support people to eat and drink, in any adult social care setting. Built on the Skills for Care statutory and mandatory training guide and Food Standards Agency guidance for care homes, it covers why food safety matters, personal hygiene and fitness to work, chilling, cooking and reheating, cross contamination, cleaning, the 14 allergens, texture modified diets, gift food, and recording and reporting. Eight lessons with scenarios and activities, then a final assessment.
Bulk discounts from 10+ licences
 Annual Certificate
General Health & Safety Awareness
Annual health and safety refresher for everyone working in adult social care, in care homes, people's own homes, supported living and day services. Built on the Skills for Care statutory and mandatory training guide and Health and Safety Executive guidance for health and social care, it covers your legal duties, risk assessment, common hazards in care, hazardous substances, security and lone working, work related stress and your own wellbeing, responding to accidents and sudden illness, and reporting. Eight lessons with scenarios and activities, then a final assessment.
Bulk discounts from 10+ licences
 Annual Certificate
Infection Prevention and Control
Annual infection prevention and control refresher for care workers in residential, nursing, home care, supported living and day services. Built on the Skills for Care statutory and mandatory training guide, NHS England's national infection prevention and control manual and the adult social care IPC resource, it covers the chain of infection, standard precautions and your role, hand hygiene, PPE, recognising and reporting infection, outbreaks, cleaning, laundry and spills, waste, sharps and exposure incidents. Eight lessons with scenarios and activities, then a final assessment.
Bulk discounts from 10+ licences
 Annual Certificate
Medication Administration and Competency
Annual medication administration refresher for care workers who support people with medicines in care homes, home care and supported living. Built on the Skills for Care statutory and mandatory training guide, NICE guidance SC1 and NG67 and CQC medicines guidance, it covers the law and your role, common medicines, consent, capacity and covert administration, preparing to administer, administration techniques, recording and monitoring, controlled drugs and storage, and errors and your limits. Eight lessons with scenarios and activities, a final assessment, then an observed practical assessment by your employer.
Bulk discounts from 10+ licences
 Annual Certificate
Mental Health Awareness
Mental health awareness for everyone working in adult social care, mapped to Tier 1 of the Mental Health Core Capabilities Framework (2026). It covers what mental health and wellbeing mean, common mental health needs, stigma, rights and trauma informed practice, communicating with people in distress, physical health and loneliness, older people and people with a learning disability or who are neurodivergent, recognising and responding to self harm and suicide, and working with families, other services and the law. Eight lessons with scenarios and activities, then a final assessment.
Bulk discounts from 10+ licences
 Annual Certificate
Moving and Handling of People
Annual moving and handling of people refresher for care workers who assist and move people in care homes, nursing homes, home care and supported living. Built on the Skills for Care statutory and mandatory training guide and Health and Safety Executive guidance, it covers the law, how backs are injured, risk assessment, safe handling principles, moving and positioning with dignity, hoists and slings, other equipment and falls, and the limits of your role. Eight lessons with scenarios and activities, a final assessment, then an observed practical assessment by your employer.
Bulk discounts from 10+ licences
Give your team gdpr / data protection training that actually sticks.
Buy your licences, allocate them in seconds, and let the evidence build itself.
Compared
Three ways to train a care team.
These modules are written and kept current by us, so your managers do not have to write or maintain them. We have compared what each approach does rather than naming providers, because products change and this should still be true next year.
| CareStream | A generic e-learning library | A trainer you book | |
|---|---|---|---|
| Try a real lesson and a real question before you buy | |||
| Learning outcomes and time to complete stated up front | |||
| Written lesson sections, each with its own illustration | |||
| Interactive exercises after the lesson that teaches them, in every module | |||
| Assessment in every module, with the key points to revisit | |||
| Taken in any of sixty plus languages | |||
| A wrong answer triggers a follow-up lesson, not just a re-sit | |||
| Practical sign-off by a manager where the subject needs it | |||
| Completion files itself into your training matrix and evidence pack | |||
| Bought one module at a time, with no annual contract |
Generic libraries are often cheaper per learner. They teach a national standard rather than being built, updated and evidenced around the way a CQC-registered service is actually inspected.
Care policies
Every module is written from a policy
If the policy behind it is out of date, the training inherits that. Sixty six policies written for your service, checked against current law and read by a person before they carry your name, from £39.